
Certification Courses
Hands-On Labs
Threat Intelligence
Latest Cyber News
MITRE ATT&CK Breakdown
All Cyber Keywords
In mid-2025, a sophisticated attack targeted the popular open-source text editor Notepad++. The China-linked Lotus Blossom hacking group (also known as Billbug, Raspberry Typhoon) breached the software's hosting provider, hijacking update traffic to deliver a previously undocumented backdoor dubbed Chrysalis. This supply chain compromise went undetected for months, affecting users across APAC, South America, and Europe. By exploiting insufficient update verification in older Notepad++ versions, the attackers selectively redirected a fraction of users to malicious servers. This breach underscores the critical need for robust software update pipelines and defense-in-depth strategies. In this beginner-friendly breakdown, we’ll dissect the entire Notepad++ supply chain attack, map it to MITRE ATT&CK, and provide actionable blue-team defenses.
The Lotus Blossom group employed a blend of tactics to maintain stealth and persistence. Below is a mapping of key techniques observed in the Notepad++ supply chain attack.
| Tactic | Technique ID | Technique Name | How It Was Used |
|---|---|---|---|
| Initial Access | T1195.001 | Supply Chain Compromise | Breached the hosting provider to modify Notepad++ update mechanism. |
| Execution | T1204.002 | User Execution (Malicious File) | Victims ran the trojanized update (update.exe) believing it was legitimate. |
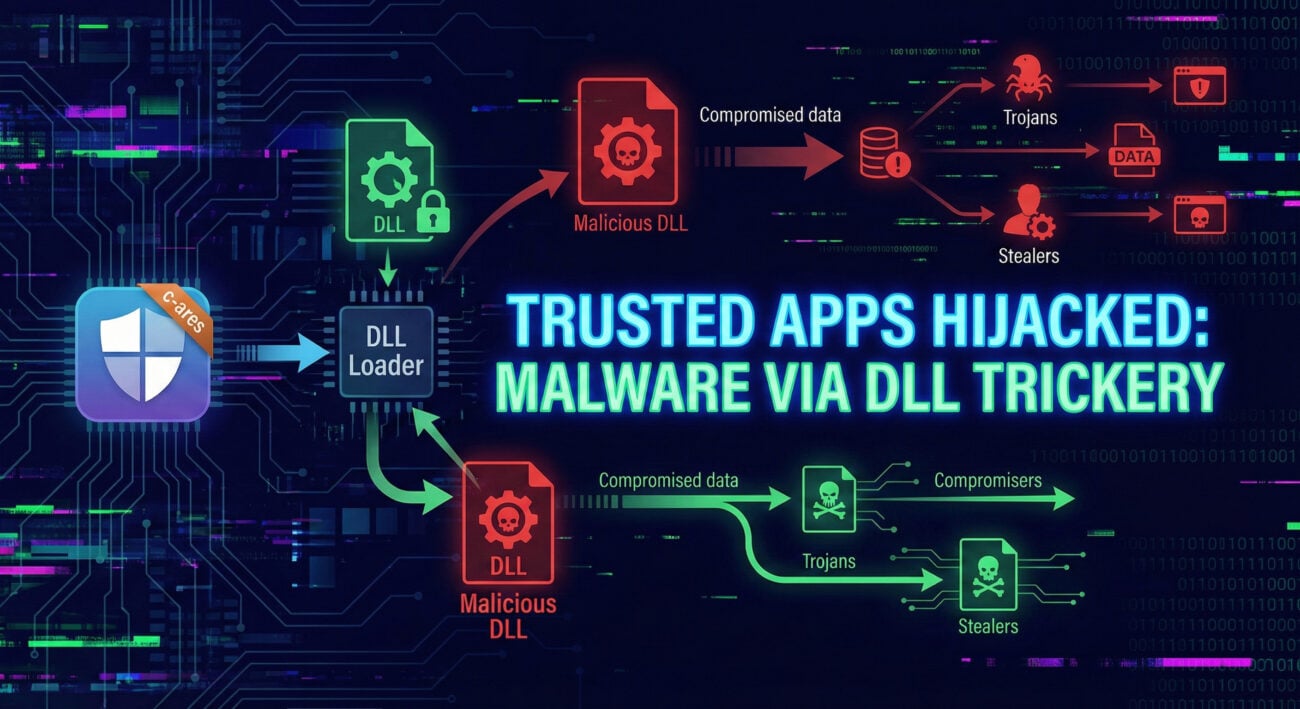
| Defense Evasion | T1574.002 | DLL Side-Loading | Used legitimate Bitdefender binary (BluetoothService.exe) to load malicious log.dll. |
| Defense Evasion | T1027 | Obfuscated Files/Info | Chrysalis backdoor used encrypted shellcode and Microsoft Warbird obfuscation. |
| Command and Control | T1071.001 | Web Protocols | Beacon contacted api.skycloudcenter[.]com over HTTP. |
| Impact | T1496 | Resource Hijacking | Backdoor allowed file exfiltration, interactive shell, and potential lateral movement. |
Understanding these techniques helps defenders spot similar behaviors in their environment.
The attackers didn’t spray malware indiscriminately, they selectively targeted high-value individuals and organizations. According to Rapid7 and Kaspersky telemetry, the Notepad++ supply chain attack victims included:
This targeting aligns with Lotus Blossom’s historic interest in political and economic intelligence. The group used the trusted Notepad++ update channel to slip past perimeter defenses, showing how supply chain attacks can bypass even strong security postures.
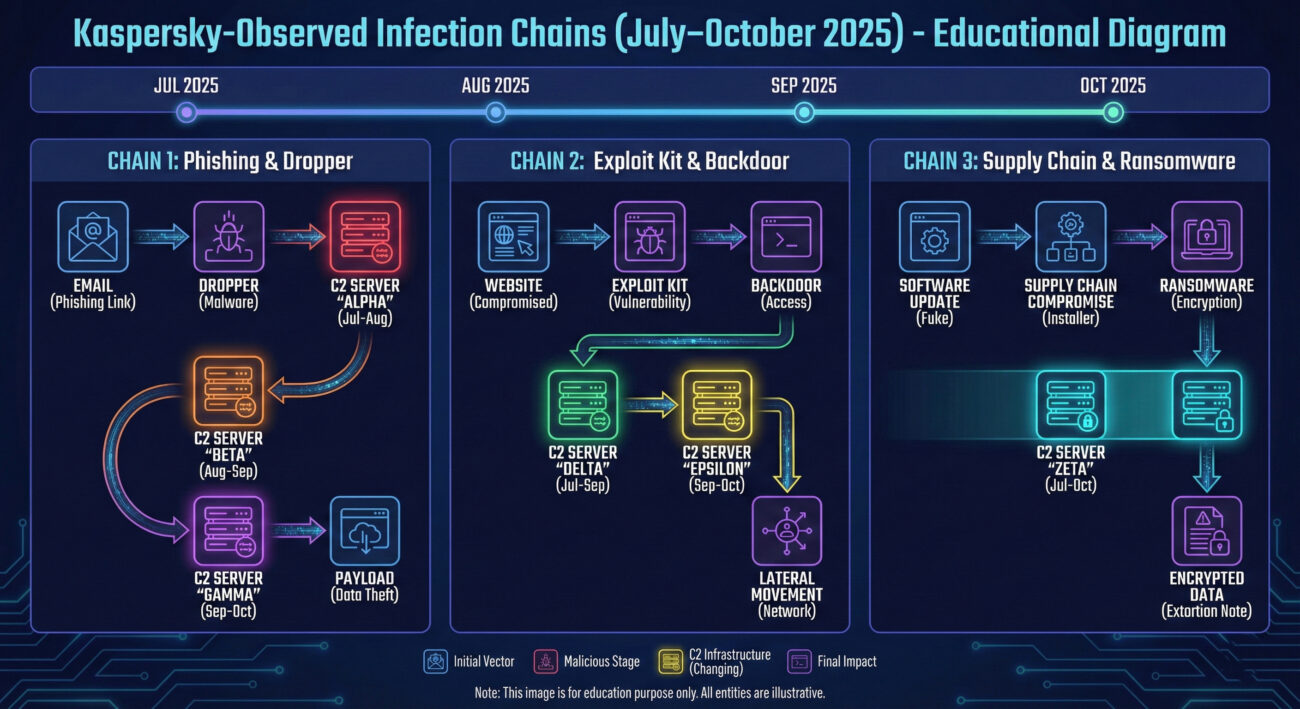
The attack evolved over several months, with three distinct infection chains. Below is a simplified flow of how the Chrysalis backdoor reached victims.
Attackers breached Notepad++’s hosting provider (unknown entity) sometime before June 2025. They gained the ability to redirect update requests from specific IP ranges to attacker-controlled servers (infrastructure hijacking). The legitimate update mechanism (GUP.exe) was left intact, but the download URL was swapped.
When victims ran Notepad++ (versions prior to 8.8.9), the updater contacted the legitimate domain, but the request was transparently redirected to malicious IPs like 95.179.213[.]0. Users downloaded a trojanized NSIS installer named update.exe (or variants like install.exe, AutoUpdater.exe).
The NSIS installer dropped two key files:
When BluetoothService.exe executed, it sideloaded log.dll (DLL side-loading: T1574.002). The DLL then decrypted and launched the final payload shellcode.
The decrypted shellcode installed the Chrysalis backdoor, a feature-rich implant capable of:
api.skycloudcenter[.]com.Later variants also fetched a Cobalt Strike beacon via a Metasploit downloader. The attackers even used Microsoft Warbird (an undocumented obfuscation framework) to hide shellcode, borrowing code from a public PoC.
Kaspersky observed three infection chains with rotating C2s and downloader tweaks, showing the group’s agility. By December 2025, the hosting provider access was terminated and Notepad++ migrated to a new provider with stronger security.
This breach offers lessons for both software maintainers and end users.
Below is a simplified diagram of the Notepad++ supply chain infection chain. The visual shows how update traffic was hijacked and the subsequent DLL side-loading.

Lotus Blossom (aka Billbug, Raspberry Typhoon) is a China-linked APT group active since at least 2012. They focus on espionage targeting government, military, and technology sectors in Southeast Asia. They frequently use DLL side-loading and public exploit code.
Indicators include: presence of update.exe in Notepad++ folders, unexpected processes like BluetoothService.exe running, or network connections to 45.76.155.202 or 95.179.213.0. Use a memory scanner or EDR to check for Cobalt Strike beacons.
Yes. The maintainers patched the update verification flaw in version 8.8.9 (December 2025) and moved to a new hosting provider. Ensure you’re running the latest version (8.8.9 or higher) and enable automatic updates.
Chrysalis is a custom implant that collects system info, provides remote shell, and can download additional payloads. It uses encrypted shellcode and was delivered via the malicious Notepad++ update.
Absolutely. Supply chain attacks are on the rise (e.g., SolarWinds, 3CX). Any software with an auto-update feature is a potential vector. That’s why defense in depth and update integrity checks are critical.
Now that you understand the mechanics of this attack, take action:
📚 External Resources for Further Reading:
© Cyber Pulse Academy. This content is provided for educational purposes only.
Always consult with security professionals for organization-specific guidance.
Every contribution moves us closer to our goal: making world-class cybersecurity education accessible to ALL.
Choose the amount of donation by yourself.